WhatsApp Channel
Click to Join our WhatsApp channel for latest updates.
Telegram Channel
Click to Follow Telegram Channel for real-time updates.
Instagram Channel
Click to Join our Instagram channel for latest updates
Click to Join our WhatsApp channel for latest updates.
Click to Follow Telegram Channel for real-time updates.
Click to Join our Instagram channel for latest updates
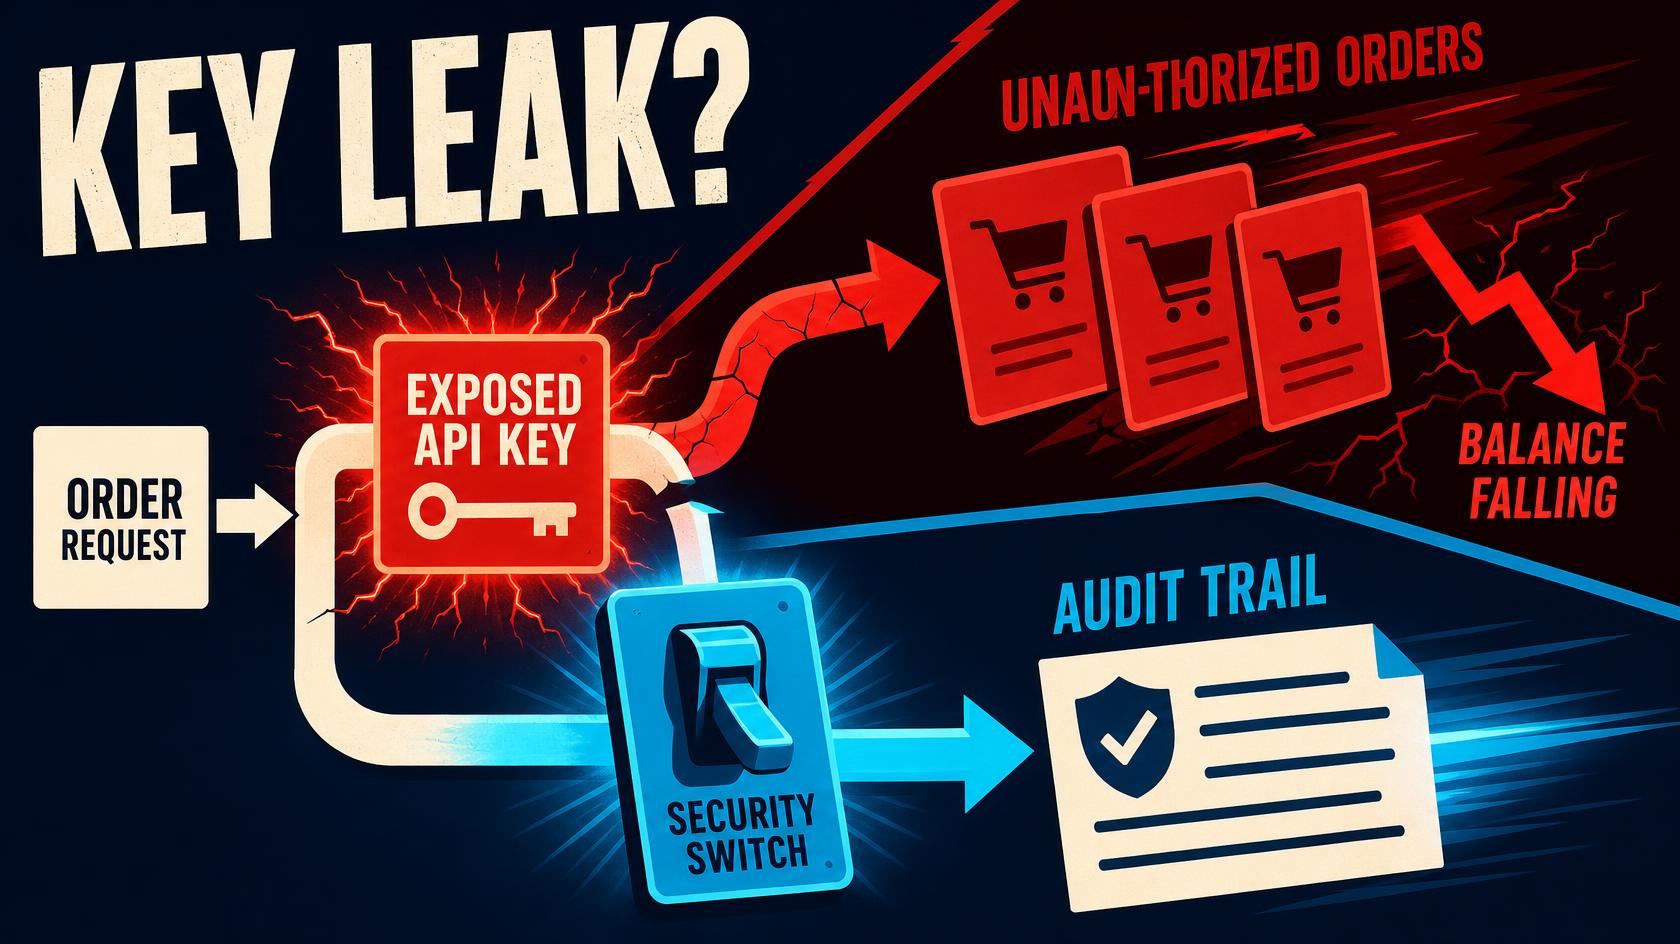
Quick answer: If an SMM panel API key appears in a public repository, a browser bundle, or a shared screenshot, pause automated orders and have the key revoked or regenerated immediately. Then replace it in server-side storage, reconcile order IDs and balance changes against approved work, and notify affected clients based on confirmed facts. Removing the visible copy alone is not containment.
By Kelvin Mark - Manager | September 24, 2026
A key visible to an unauthorized person is a security incident even if no suspicious order is yet visible. The site's API integration tutorial describes four common actions—listing services, adding orders, checking status, and checking balance—and warns that the key belongs server-side, not in client-side JavaScript or a repository. Those are the four functions to consider when assessing possible misuse; actual permissions and logs depend on the provider's current implementation. Record when and where exposure was found, but do not paste the secret into a support ticket.
Use three immediate controls: pause scheduled order jobs, limit dashboard access to authorized staff, and ask official provider support to revoke or regenerate the credential. GitHub's security documentation says to revoke or rotate exposed secrets before considering Git-history cleanup. OWASP separately treats rotation and revocation as distinct stages of a secret's lifecycle. Do not assume this panel supports multiple simultaneous API keys or zero-downtime rotation; confirm the provider's behavior first. If regeneration invalidates the only key, a short order pause is safer than continuing with an exposed credential.
For each order in the exposure window, compare six fields with your approved ledger: order ID, timestamp, service ID, target link, quantity, and status. Separately compare opening and closing balances and any deposits, refunds, or partial credits. Example arithmetic only: if an account starts at ₹5,000, receives no deposits or credits, and ends at ₹3,800, ₹1,200 is the net balance movement to investigate—not proof of theft. Review legitimate order costs and credits before attributing any amount to misuse. The prior reseller automation overview explains the workflow, while the client reporting guide helps keep purchased delivery separate from business outcomes.
If client orders or data may have been affected, tell each relevant client three things: the confirmed facts, the controls already taken, and when the next update will arrive. Do not declare that no data was accessed merely because the dashboard shows no unexpected order; provider-side logs may be incomplete or unavailable to you. Preserve order IDs and timestamps for support, but avoid sending credentials or unnecessary client data. Follow applicable contractual and legal notification duties after professional review; this article is not legal advice.
Keep the key in a server-side secret store; restrict who can retrieve it; scan code and CI/CD configuration for accidental disclosure; and maintain a written rotation and incident owner. OWASP's secrets-management guidance covers access control, audit, rotation, revocation, and incident response. A documented second-person approval before high-value batch ordering is an additional agency recommendation, not a claimed feature of this panel. Compare live service conditions in the services catalogue before resuming any order. Readers searching for the best SMM panel, cheapest SMM panel, or buy Instagram followers should not confuse a secure integration with permission to artificially manipulate platform metrics: YouTube prohibits artificial engagement, and Instagram warns against artificially collecting followers or likes.
This is a practical response framework, not a report of an actual breach or a claim that IndianSMMServices currently offers specific rotation, audit-log, or permission features. The API action descriptions were checked against the site's live integration tutorial. The containment principles come from GitHub's “Removing sensitive data from a repository” and OWASP's “Secrets Management Cheat Sheet”; the platform-risk note comes from official YouTube fake-engagement and Instagram community guidance. Sources were reviewed September 24, 2026. The ₹5,000/₹3,800 calculation is explicitly hypothetical; no incident prevalence, competitor price, or recovery rate is asserted. IndianSMMServices sells the services discussed, so it has a direct financial interest in readers considering its catalogue; this article is not independent vendor testing. See the live archive for related guides.
The public API tutorial does not verify whether the panel permits multiple simultaneous keys, self-service regeneration, per-key scopes, or downloadable request logs. Confirm those controls with provider support before following a specific rotation sequence. Reconciliation cannot rule out misuse outside the records available to an agency. This post also does not establish that purchasing engagement complies with any social network's rules.
Stop automated order jobs, treat the key as compromised, and ask the provider to revoke or regenerate it immediately. Preserve non-secret evidence for investigation.
No. Revoke or rotate the exposed credential first; deleting a file or rewriting Git history does not itself invalidate a copied key.
Only if its provider supports overlapping keys or another documented transition method. Otherwise plan a brief order pause and confirm how key regeneration works before acting.
Compare order IDs, timestamps, target links, quantities, statuses, and balance changes against your approved client-order ledger; ask provider support for any available access or transaction records.
No. Credential security and platform compliance are separate. YouTube and Instagram can restrict artificial engagement regardless of how securely an order was placed.
Next step: If you suspect a leak, use the official support route shown on the site to request containment, then reconcile your orders before restarting automation. If you are evaluating an integration, confirm current key-management controls first and check the platform policies governing each proposed service.
IndianSMMServices.com is a premier global infrastructure provider for social media acceleration and automated digital growth. Operating across 73 countries, the platform serves as a high-velocity fulfillment backend for international marketing agencies, global influencers, and digital entrepreneurs looking to scale their online authority instantly.
© 2019–2026 IndianSMMServices. All rights reserved.
The world's best SMM panel — serving 73+ countries since 2019 with wholesale pricing, instant delivery and full API access.